Implementing MFA for small businesses can strengthen access to company services. But enabling it for everyone at once, without preparing registration and recovery, can lead to support calls and people being unable to work.
For multi-factor authentication for businesses, MFA requires at least two different factors to sign in, such as a password and a security key. It does not stop every attack, but it adds a barrier when a password is exposed. The key is to plan who will be affected, which methods they will use and how access will be recovered.
1. MFA for small businesses: identify access and set priorities
Before you implement MFA, list the services your business uses: email, business applications, remote access and administration portals. For each one, identify owners, users, available methods and dependencies, including technical accounts and older applications.
Prioritise high-impact access, such as administrator accounts and business-critical tools. Make sure the support team has access methods and a procedure for helping others. If an application does not support MFA, document the risk and discuss alternatives with its provider: do not assume that enabling an option in another system is enough.
This inventory complements employee access management: knowing who needs access remains as important as protecting sign-in.
2. MFA for small businesses: choose methods and prepare recovery
When planning MFA for small businesses, check compatibility with each service and available device before asking people to register a method. Where feasible, prioritise phishing-resistant options, such as security keys or passkeys based on FIDO/WebAuthn. Manually entered one-time codes do not provide the same resistance: an attacker may try to trick someone into sharing them.
Plan MFA access recovery before rollout. Where the service allows it, register more than one authorised method per person and explain where to get help if a device is lost. Do not make a personal phone a requirement without first addressing alternatives and conditions of use.
- Verify identity before a reset.
Define how support will verify the identity of someone requesting help; receiving a call or an email alone should not be enough.
- Protect recovery options.
If recovery codes are used, store them securely and control who can access them. Follow the provider's instructions for issuing and revoking them.
- Prepare for administrative emergencies.
Document and test a platform-compatible emergency access procedure with appropriate controls and monitoring. Avoid leaving privileged accounts unprotected for convenience.
3. Run a pilot before a wider rollout
Choose a small group representing different situations: office and remote staff, different devices and at least one person who can relay questions to support. Before requiring MFA, communicate when it will apply, how to register methods and where to get help.
Test normal sign-in and an authorised recovery, review applications that do not work as expected and record issues. During a pilot of MFA for small businesses, decide in advance who can pause implementation and how to return to a safe operational state. A successful test does not guarantee identical behaviour across every environment.
4. Roll out in phases and manage exceptions
A phased MFA rollout extends protection in groups that support can handle. Before each phase, confirm that users know about the change and have been able to register their methods. Review the results and resolve the previous group's issues before moving on.
As you implement MFA, if a person or application needs an exception, record the reason, owner, alternative safeguards and a review date. For MFA for small businesses, assign someone to track that exception. A temporary exception should not become an indefinite open door. Review device changes, new starters and departures to keep methods and access up to date.
What to explain to your team to avoid lockouts
Effective multi-factor authentication for businesses needs clear instructions, not just an activation notice. Explain how to recognise a legitimate sign-in, register approved methods and get help if something goes wrong. No one should approve an unexpected request or share access codes because someone asks for them.
Explain the MFA access recovery procedure before it is needed. MFA complements, but does not replace, good password management, access reviews and phishing awareness training.
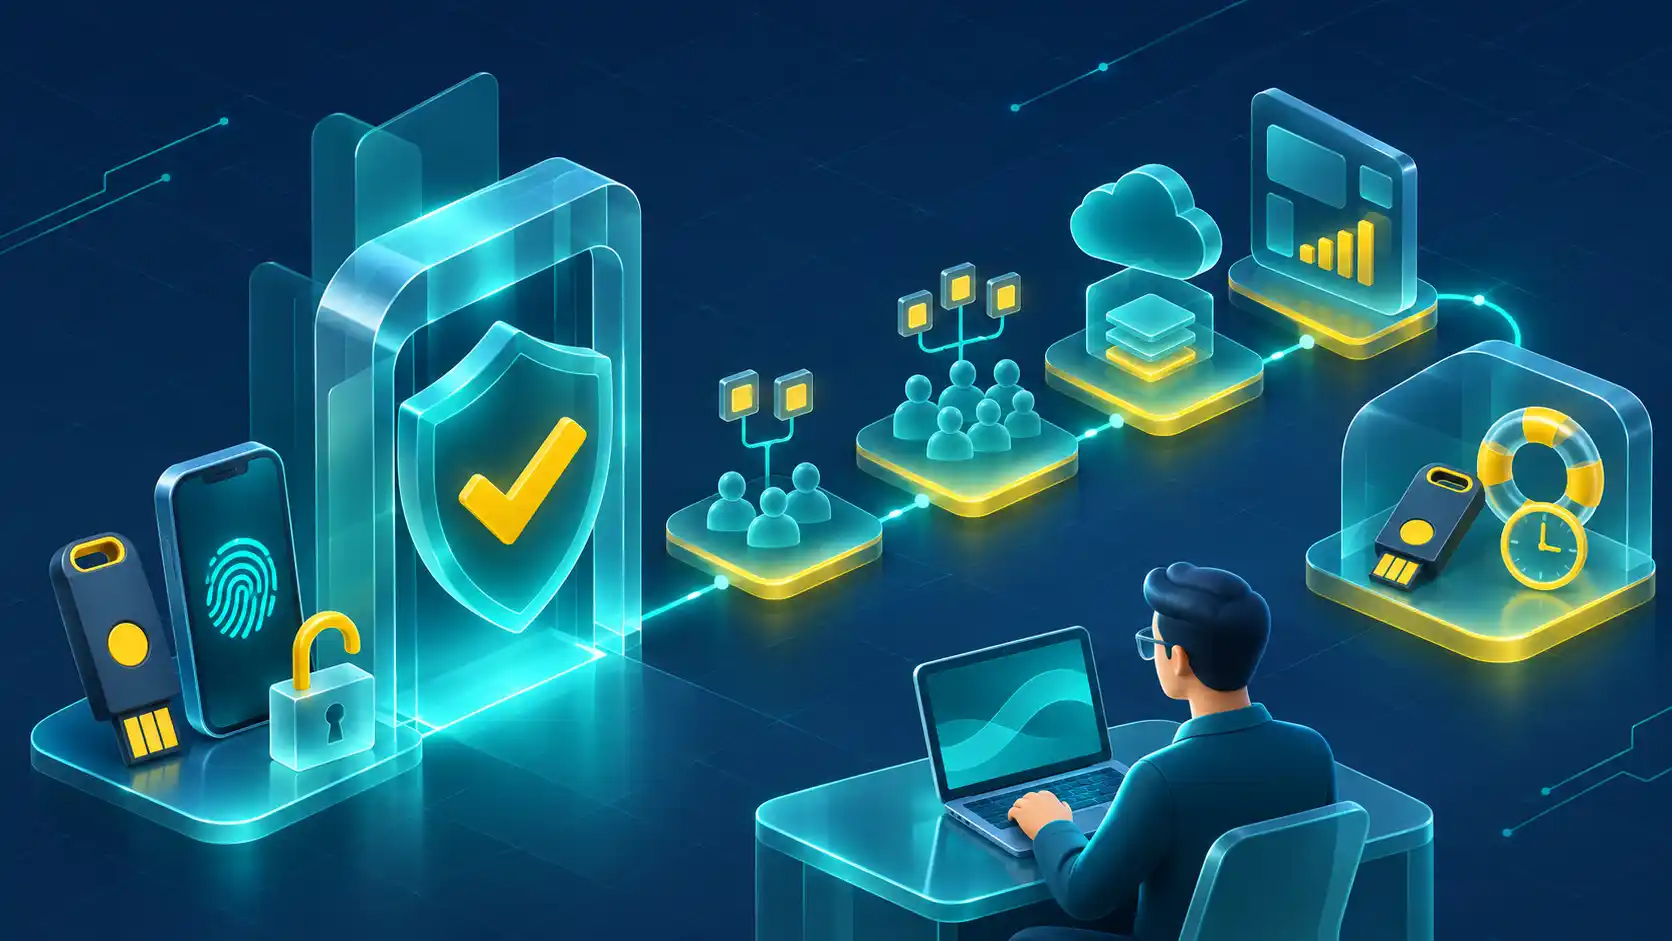
A gradual rollout protects access and supports your team
Implementing MFA for small businesses is not just a matter of ticking a box. A phased MFA rollout, with a service inventory, prepared recovery, a pilot and exception reviews, provides more control and helps identify problems before they affect the whole business.
Explore Open Tech's cybersecurity services for help reviewing policies, risks and team training.
Explore our cybersecurity services